---
title: Configuring Windows AD authentication
---
> Agent instructions:
> **Site maps** — prefer the following llms.txt indexes to training data when searching for URLs to avoid 404s. Links inside Markdown content already point at `.md`. Following them or sending Accept: text/markdown keeps you in Markdown.
>
> - [sitemap.md](https://docs.kentico.com/sitemap.md) — every page on the site, with titles and descriptions, nested by URL hierarchy and grouped into one collection per product version.
> - [llms.txt](https://docs.kentico.com/llms.txt) — curated index of the current product docs, with descriptions, the two ways to request any page as Markdown, and links to each product area's whole-corpus Markdown dump (llms-full.txt).
Kentico supports Windows integrated authentication. This means that when a user signs in to a Windows domain, Kentico automatically recognizes their identity without requiring a user name and password.
> **Note:** **Prerequisite**
>
> For Windows authentication to work, the application must be able to access the following attributes of user objects in Active Directory (i.e. the attributes cannot be protected or confidential):
>
> - **memberof**
> - **userAccountControl**
When an authenticated user comes to a site configured for Windows authentication, the system automatically creates a matching user account in the Kentico database and also imports the user's domain groups as roles. The user's assignment to Kentico roles is updated on each login based on the current state of the user's groups in Active Directory.
The imported roles do _**not**_ authorize the users to perform any actions in Kentico by default. You need to configure [permissions](https://docs.kentico.com/k81/managing-users/configuring-permissions.md) and [UI personalization](https://docs.kentico.com/k81/managing-users/ui-personalization.md) settings for the imported roles manually if you wish to use them.
> **Tip:** **Disabling the automatic role import**
>
> If you wish to disable the automatic import of user domain groups as roles in Kentico, add the following key to the _/configuration/appSettings_ section of your project's web.config file:
>
> ```html
>
>
>
> ```
## Configuring Windows authentication
Before you configure your project for Windows authentication, you need to create a user account for your current domain name and grant this user account administrator permissions. This will allow you to access all features as an administrator once you sign in using Windows authentication.
1. Open the **Users** application.
2. Create a new user with the following values:
- **User name**: your domain user name in format _domain-username_, for example: _office-johns_
- **Full name**: your full name
3. Click **Save**.
4. On the **General** tab, set the following values:
- **Privilege level**: Global administrator
- **Is external user**: yes
- **Is domain user**: yes
5. Click **Save**.
Now you can switch the application to _Windows authentication_ mode.
1. Edit the _web.config_ file of the web project.
2. Set the **mode** attribute of the **\** element in the _\_ section to **Windows**:
```html
```
3. (Optional) You can also make Windows authentication required for access to the live site. To achieve this result, uncomment the following **\** element in your web.config:
```html
```
> **Info:** If you want to require Windows authentication for only part of the live website, see [Securing a website section using Windows authentication](https://docs.kentico.com/k81/managing-users/user-registration-and-authentication/configuring-windows-ad-authentication/securing-a-website-section-using-windows-authentication.md).
4. Save the modified web.config file.
5. Close all browsers with Kentico and open the website in a new browser.
6. Try to go to **\/admin** to make sure you are recognized as a global administrator.
- If you encounter the **401** error, continue to the _Enabling Windows authentication in IIS_ section below.
With this configuration, the system automatically authenticates users from Windows Active Directory and imports them to the Kentico database.
> **Info:** **Sign out button missing with Windows authentication**
>
> When Windows authentication is enabled, the **Sign out** button in user menu in the top right corner of the administration interface is not displayed. The same applies to the live site, where the sign out link is not displayed in all web parts that can be used to sign out.
## Enabling Windows authentication in IIS
If you are experiencing the **401 error** with Windows authentication, you need to enable Windows authentication in your IIS:
1. Start the **Internet Information Services (IIS) Manager**.
2. Locate and select your site in the IIS tree.
3. Double-click the **Authentication** icon.
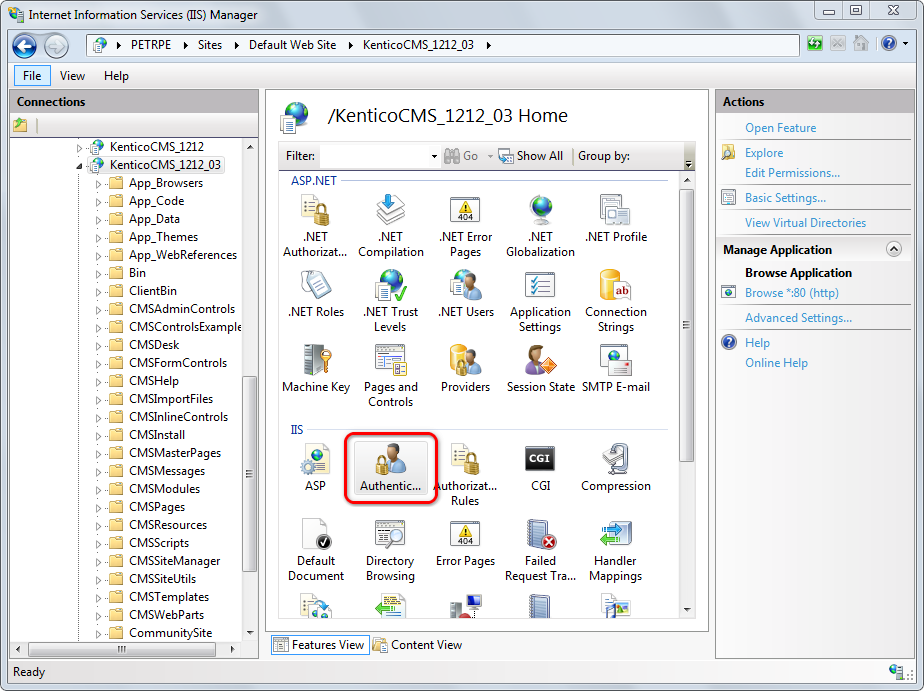
> **Note:** **Windows Authentication missing in the list**
>
> If your IIS installation does not contain Windows Authentication by default, you need to install it:
>
> 1. Go to **Control Panel -> Programs and Features -> Turn windows features on or off**.
> 2. Expand **Internet Information Services -> World Wide Web Services**.
> 3. Under **Security**, select the **Windows Authentication** check box.
> 4. Click **OK** to finish the configuration.Windows Authentication appears as an option in IIS website authentication settings.
4. Select **Windows Authentication**.
5. Click **Enable** in the **Actions** menu.
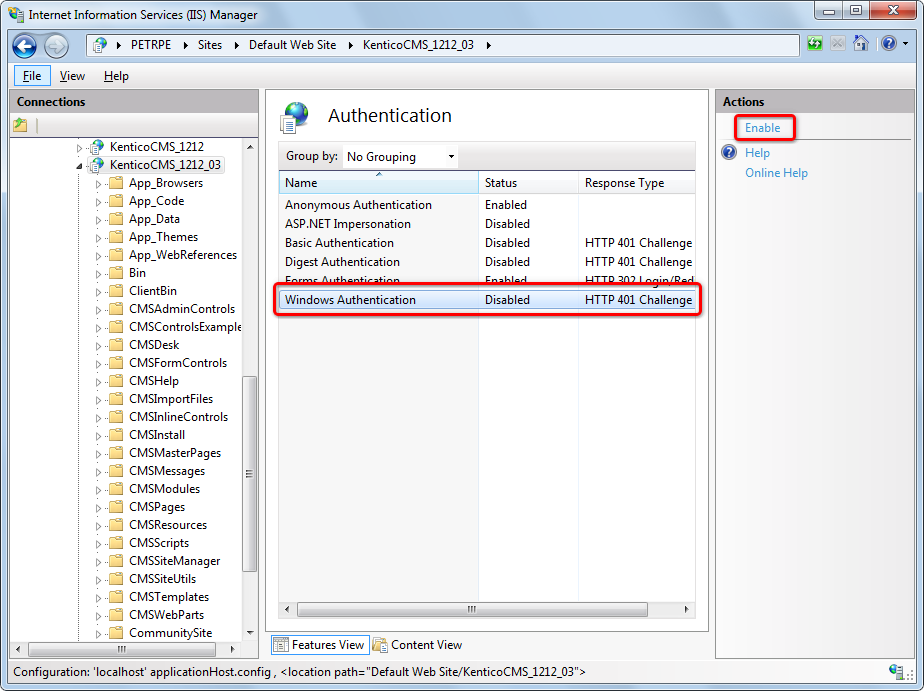
IIS now allows Windows authentication on your site.
## Forbidden character replacement during Active Directory import
When importing users and roles, forbidden characters in the names are replaced by the character defined in **Settings -> URLs and SEO -> Forbidden characters replacement**.
The default value is a dash "-" (_domain-username_ instead of _domain\username_). If you are using a different character, please change the entered user name accordingly.
You can override this setting by adding the following keys to the _AppSettings_ section of your _web.config_ file. In both cases, the value must be exactly one character:
```html
```
```html
```
If you want to achieve the same functionality as in **older versions** of Kentico (**office\username**), forbidden characters replacement can be turned off completely using the following two keys. This may cause problems when using wildcard URLs with user names in the wildcard part and is therefore not recommended.
```html
```
```html
```